A surprise announcement from Tesla CEO Elon Musk has confirmed that the electric automaker will phase down Cybertruck assembly operations at its Austin, Texas manufacturing facility in 2026, to free up production capacity for the company’s upcoming fully autonomous Cybercab robotaxi line. Musk did not explicitly clarify whether the bold, angular pickup would be permanently discontinued entirely or shifted to a separate production site elsewhere in Tesla’s global network, but public comments from the vehicle program’s lead engineer Wes Morrill on X appeared to frame the Cybertruck as a completed development milestone rather than an ongoing mass-market product, noting that the model “was an incredible technology development platform and lives on through Cybercab.”
The polarizing stainless-steel pickup, first unveiled to massive fanfare in a 2019 live event that became infamous when Musk’s on-stage demonstration of its “unbreakable” armored glass resulted in two immediate, highly publicized shatters, has had a turbulent lifecycle from its inception. The launch was repeatedly pushed back years past its initial target, finally reaching consumer driveways in late 2023, after Musk reported over 146,000 pre-orders flooded in within days of the 2019 reveal. Admirers lauded its retro-futuristic, Blade Runner-esque geometric design, with a loyal cohort of Tesla superfans hailing it as the most innovative vehicle the brand had ever built, but the model faced persistent headwinds: widespread mockery of its unconventional aesthetic from critics, multiple safety recalls including a 2025 action affecting over 46,000 units over loose exterior trim risks, and a steep price point that started at $61,000 for the base fully loaded configuration and now tops out at $102,000 for the high-performance Cyberbeast variant. Actual sales volumes have underperformed internal and industry expectations, failing to carve out a significant foothold in the highly profitable U.S. full-size pickup truck segment that is dominated by legacy gas-powered and competing electric models from Ford and GM.
The news of the Texas production wind-down has sparked an outpouring of grief and frustration across Tesla’s global online fan communities, with dozens of users sharing tributes to the vehicle and expressing dismay at its apparent imminent discontinuation. When one prominent fan posted a lament calling the Cybertruck “the best vehicle Tesla has ever made” and mourning its planned exit from production next year, Musk replied with a one-word confirmation: “true”, before adding a reassuring note that the existing global Cybertruck fleet will remain on roads for decades to come. Musk himself has repeatedly framed the Cybertruck as a personal passion project, describing it as “way more awesome than people realise” in a March public appearance and calling it “the best product Tesla has ever made to date” in a subsequent April statement, even as industry analysts long questioned whether mainstream U.S. truck buyers would embrace its radical design and premium price tag over more conventional, established pickup offerings.
分类: technology
-
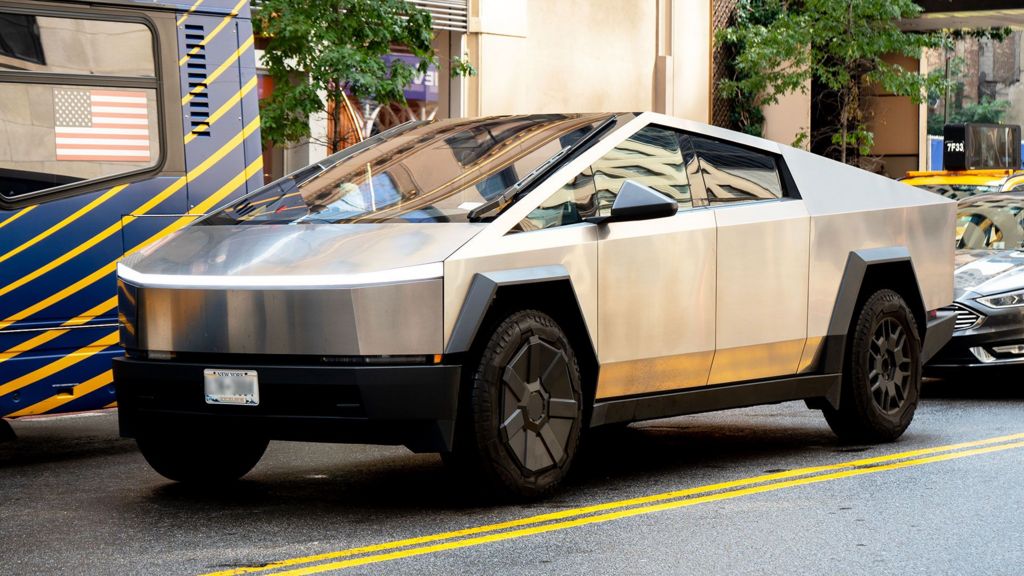
Elon Musk appears to signal the end of the road for Cybertruck
-
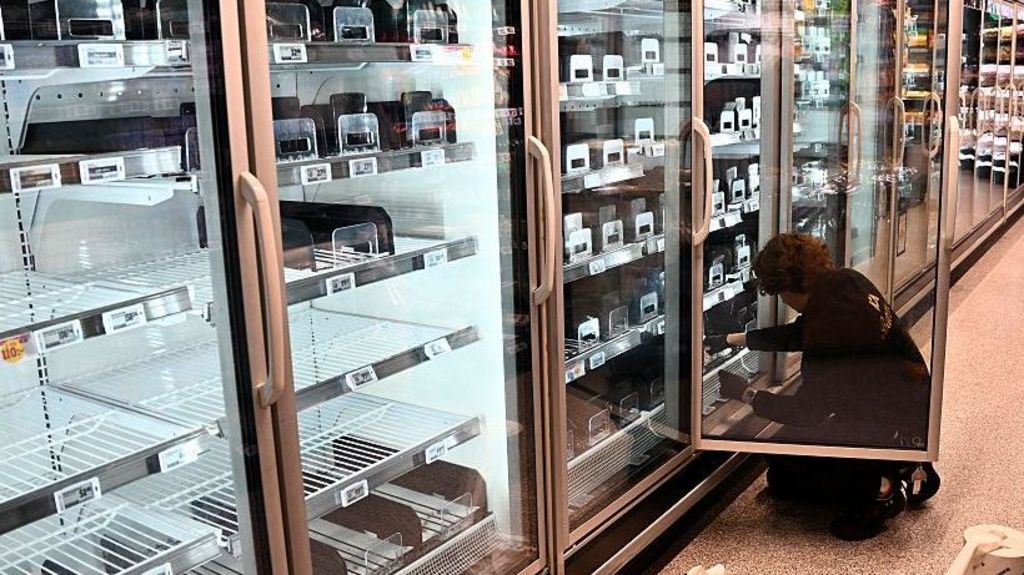
French blood storage impacted by freezer hacks as theories swirl about culprits
A previously unreported wave of recent cyber-intrusions targeting internet-connected refrigeration units in Europe has expanded beyond the initially known supermarket sector, French health authorities confirmed this week. Operators of the French Blood Establishment (EFS) revealed that regulated cold storage rooms holding life-saving donated blood supplies were among the compromised systems, where unidentified threat actors attempted to raise internal temperatures to ruin critical blood products. Rapid, proactive intervention by on-site EFS staff prevented any loss of blood inventory, and health officials have verified zero adverse impacts on patient safety to date. Prior to this disclosure, public awareness of the hack campaign was limited exclusively to disruptions affecting European grocery chain freezer units.
Unsubstantiated online claims have circulated linking the attacks to two Russia-affiliated hacktivist collectives, NoName057(16) and the Z-Pentest Alliance, which posted statements claiming responsibility for breaching systems manufactured by industrial control firm Danfoss, a leading supplier of refrigeration management components. However, independent cybersecurity analysts have cast significant doubt on these assertions, noting that NoName057(16) has a well-documented history of claiming credit for operations it did not execute, and its demonstrated technical capabilities are largely limited to basic distributed denial-of-service (DDoS) traffic flooding attacks, rather than the targeted industrial system intrusions seen in this campaign.
To trace the origin and tactics of the threat actors, three separate cybersecurity firms have deployed specialized digital decoy tools known as “honeypots” across global networks: fake, intentionally vulnerable refrigeration management software instances designed to lure hackers into revealing their scanning patterns, access methods, and operational infrastructure. Teams from Spanish cybersecurity firm Previdian, Scotland-headquartered Lupovis, and French national cyber-defense provider Sekoia have all gathered actionable intelligence from these traps.
Evidence collected from the honeypots shows the second major wave of attacks was highly geographically targeted: Lupovis reported that its decoy systems located in Africa, South America, and even Ukraine received zero probing activity, while all scanning attempts were directed exclusively at European-based fake refrigeration units, starting 10 full days before the second round of intrusions was launched. Researchers confirmed that the targeted refrigeration control devices relied on poorly secured, publicly exposed software with widely documented, easily exploitable vulnerabilities that are openly shared on underground cybercriminal forums.
Ryan Dewhurst, a cybersecurity researcher at Previdian, emphasized that the simultaneous, overnight execution of temperature adjustments across dozens of unconnected facilities required significant pre-planning: actors had to first compile a complete list of public IP addresses for all targeted refrigeration units, coordinate access attempts across time zones, and schedule operations for off-hours to maximize potential product loss and operational disruption.
While investigators have not formally ruled out Russia-linked state actors or hacktivists, Sekoia’s public threat assessment notes that Iran-aligned hacking groups have a long, well-documented track record of targeting internet-connected industrial control systems, including a 2022 breach that compromised 40 Danfoss-managed supermarket refrigeration units in Israel, and a separate late-August 2024 incident that forced freezer systems at six U.S. military bases into full defrost mode. No technical evidence to date has confirmed Russian-speaking threat actors were behind the European refrigeration hacks, Sekoia officials confirmed to reporters.
Investigators also have not dismissed the possibility that a coordinated group of adolescent threat actors, or even unrelated copycat hacking teams, could be responsible for the different waves of intrusions. All three cybersecurity research teams noted that a sufficiently organized group with the required level of operational planning would almost certainly post public boasts of their activity on underground forums in the near future, if they had orchestrated the high-profile campaign. National law enforcement and cybersecurity agencies across multiple European countries have issued formal alerts to supermarket operators, medical facilities, and industrial sites to patch exposed refrigeration control systems and monitor for unusual temperature adjustments, as the investigation to formally identify the perpetrators remains ongoing.
-
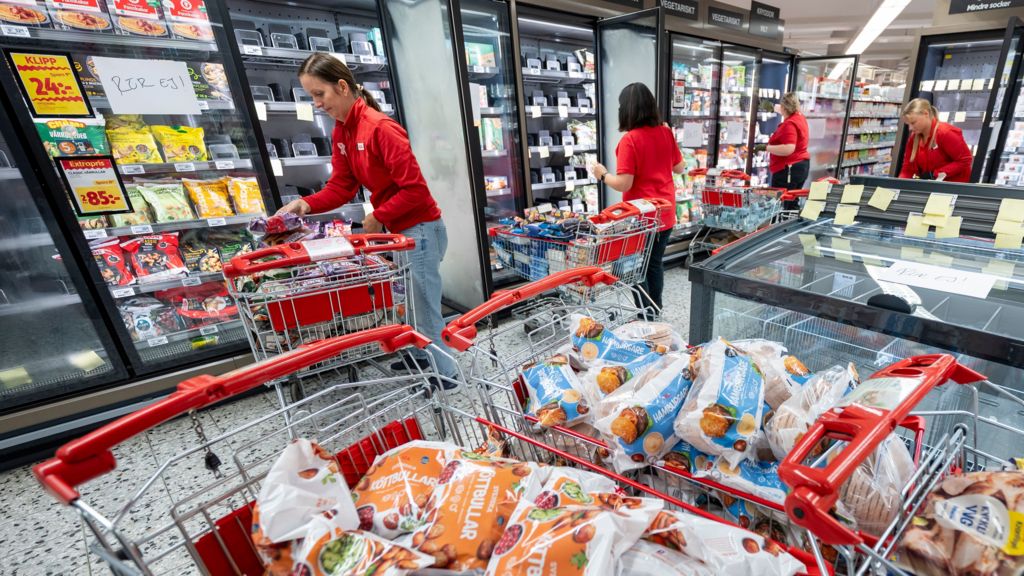
Europe on alert after supermarket freezers hit by cyber-attacks in nine countries
A sweeping wave of coordinated cyber intrusions targeting grocery retail infrastructure unfolded across at least nine European nations on Monday, triggering widespread disruptions to remotely managed refrigeration and freezer systems that pushed internal temperatures as high as 50°C (122°F) and forced operators to discard massive volumes of perishable chilled and frozen stock. The incident has spurred EU authorities to raise urgent alarms over deliberate attempts to destabilize the bloc’s critical food supply chain, coming just three weeks after a separate cyberattack crippled operations at roughly 700 French grocery outlets, resulting in tens of millions of euros in estimated food waste losses.
Across affected jurisdictions spanning Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal and Sweden, local law enforcement and cybersecurity agencies have launched formal investigations to identify the perpetrators, as no group has yet claimed responsibility for the coordinated intrusions. The string of attacks has amplified longstanding concerns over the vulnerability of internet-connected operational technology, including remote refrigeration monitoring tools, to state-backed hybrid warfare tactics that target civilian critical infrastructure to disrupt daily life without triggering conventional armed conflict.
EU Food and Agriculture Commissioner Christophe Hansen emphasized that the European Commission is treating the series of incidents with utmost gravity, issuing a public warning that additional disruptive cyber events targeting essential civilian services could occur in the near future. Commission spokesperson Thomas Regnier declined to assign formal blame for the attacks publicly, but noted the incidents serve as a stark reminder of how easily malicious cyber activity can upend core public services and directly impact ordinary residents. He stressed that EU member states must adopt a unified, proactive stance to build collective cyber resilience and prepare for comparable future threats.
National responses across the bloc have varied by the scale of local disruption. In Italy, Prime Minister Giorgia Meloni’s administration convened an emergency meeting with national intelligence leadership, noting that the immediate impact of the attacks remained very limited, as the vast majority of the country’s food distribution network runs on up-to-date cybersecurity systems capable of repelling such intrusions. Italy’s national cybersecurity agency confirmed that only four Co-op supermarket locations in Sicily and one retail outlet in Tuscany experienced disruptions, with the prime minister’s office disclosing that all affected sites relied on outdated, poorly secured systems with internet-exposed interfaces and insufficient identity verification protocols.
Belgium reported some of the most severe impacts, with dozens of supermarket locations facing total refrigeration failures, prompting federal prosecutors to open a full criminal investigation. Delhaize supermarket manager Mathieu Tilman expressed profound distress at the attack’s consequences, stating, “I cannot fathom why anyone would do this… It is deeply upsetting to see so much perfectly good food go to waste. Moments like this make you want to walk away from the job entirely.”
In Ireland, retail group Musgrave confirmed that 13 of its SuperValu locations were hit by the cyber incident, with a spokesperson noting that restocking of chilled and frozen product lines at affected outlets was already well underway by Monday. A small number of independent convenience stores in the Netherlands also reported minor operational disruptions, coming on the heels of a separate cyberattack on major Dutch supermarket chain Albert Heijn last month that forced the firm to take multiple in-store services offline. In Portugal, the Mosqueteiros group disclosed that disruptions at seven Intermarché locations were linked to the cyber campaign, which appeared to target a third-party external service provider that manages refrigeration system operations for multiple retail clients. Swedish grocery chain ICA acknowledged that a small subset of its stores experienced unusual refrigeration performance, stopping short of formally confirming a cyberattack, while Sweden’s national cybersecurity agency has launched ongoing monitoring of the situation. Finnish retail conglomerate Kesko reported abnormal temperature readings at a handful of its smaller grocery stores and is conducting internal investigations to trace the root cause, while Estonian public broadcaster ERR confirmed that at least one national supermarket location was hacked, with perpetrators deliberately raising refrigeration unit temperatures to 50°C.
Across the English Channel, the UK’s National Cyber Security Centre (NCSC) has issued an urgent advisory to all British food retailers, mandating immediate software updates for all remote fridge and freezer temperature control systems. NCSC director Richard Horne warned during an appearance on BBC Radio 4’s Today programme that the UK faces a high likelihood of an AI-powered cyberattack targeting critical national infrastructure within the next two years. Horne confirmed that the NCSC has already identified a small number of instances in the UK where vulnerable connected food supply chain technology has been exploited by malicious actors, and agency teams have been working around the clock to alert all organizations across the entire food distribution ecosystem that run exposed, unpatched systems at high risk of similar intrusions.
-
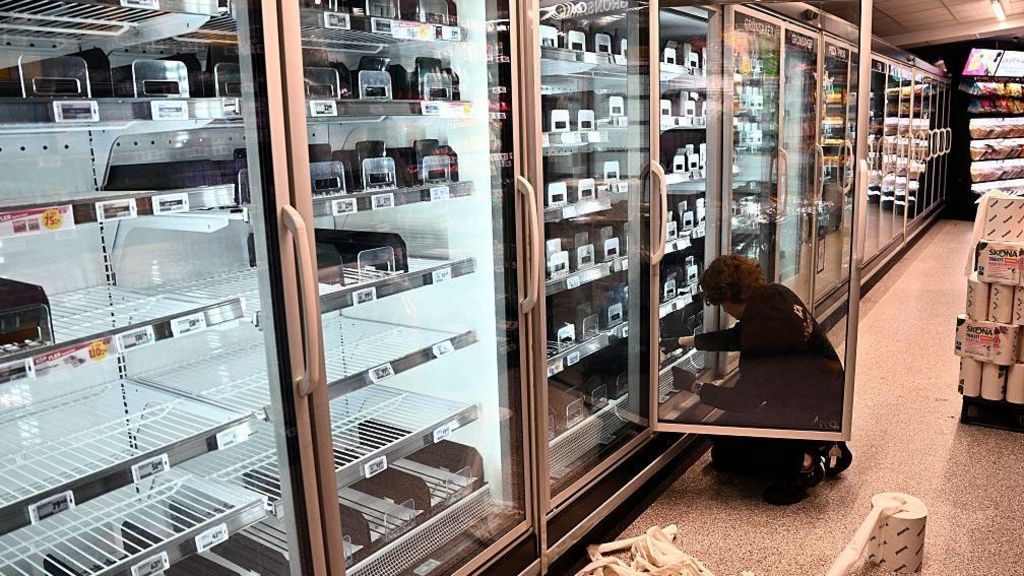
UK food supply chain affected by European freezer hacks, cyber chief says
A wave of coordinated cyber intrusions targeting remotely managed commercial refrigeration systems has struck food retail and supply chain operations across multiple European nations this week, following a similar large-scale attack in France earlier this October. First reported on Monday, the latest incidents saw threat actors exploit publicly documented vulnerabilities in cold storage control hardware to override temperature settings, switching thousands of supermarket fridge and freezer units to defrost mode and rendering large volumes of perishable fresh and frozen stock unfit for sale.
Countries including Ireland, Sweden, Estonia, Belgium, the Netherlands and Finland confirmed cases of impacted retail locations, with roughly 40 Delhaize supermarket branches across Belgium and Luxembourg reporting disruptions. Belgian refrigeration manufacturer Sabcobel verified that the attacks forced the evaporator components of connected cooling units into defrost cycles, causing rapid, unplanned temperature spikes. The attack vector matches the modus operandi used in early October, when hundreds of French supermarkets were targeted in an overnight hack that destroyed millions of euros worth of food inventory.
In the United Kingdom, the National Cyber Security Centre (NCSC) disclosed that its teams worked through the overnight hours ahead of Tuesday to alert potentially at-risk food sector organisations, after identifying a small number of cases where unpatched, vulnerable refrigeration technology had been exposed to exploitation. No major stock losses have been confirmed in the UK to date, but industry groups have flagged that food supply chain operators across the country are at heightened risk. The British Association of Independent Meat Suppliers (AIMS), which represents more than 300 meat processing and distribution firms, confirmed some of its members had become unintended collateral targets of the ongoing campaign, though no member reported full loss of perishable meat stock.
AIMS head of communications Tony Goodger emphasized that the attacks serve as a critical wake-up call for every stakeholder across the food supply ecosystem, urging full industry vigilance to address unaddressed security gaps. NCSC chief executive Dr Richard Horne noted that it remains too early to attribute the attacks to a specific threat actor, but highlighted a systemic, industry-wide failure to invest in securing legacy operational technology that underpins critical daily services. Horne warned that many organisations continue to run outdated, end-of-life refrigeration and industrial control systems that are never disconnected from public internet networks or segmented into secure, isolated environments, creating easily exploitable “low-hanging fruit” for hackers. He added that the growing accessibility of generative AI tools for malicious actors is accelerating the speed and scale at which these unpatched vulnerabilities can be located and weaponized.
Horne called on all private sector operators to prioritize upgrades for ageing connected infrastructure, noting that while government cybersecurity agencies can provide guidance and intervention support, ultimate responsibility for protecting operational systems falls to the businesses themselves. The British Retail Consortium confirmed that major UK supermarket chains including Asda, Lidl, M&S, Sainsbury’s and Tesco are collaborating closely with the NCSC to audit and harden their refrigeration control systems against potential follow-on attacks, noting that retailers have already made substantial ongoing investments in cybersecurity frameworks.
For frontline food retailers, the human and economic cost of the attacks has been particularly acute. Mathieu Tilman, who operates an independent Delhaize franchise in Belgium, described the mass disposal of hundreds of thousands of euros worth of edible, recently spoiled food as deeply distressing, noting that widespread global food insecurity makes the unnecessary waste feel profoundly unethical, to the point he considered abandoning his business entirely in the immediate aftermath of the breach.
-
Legal challenge to Australia’s social media ban to start in High Court
A two-day pivotal hearing commences Tuesday before Australia’s High Court, marking the first major judicial review of the nation’s unprecedented global-first policy that prohibits social media access for all users under the age of 16. The dual consolidated legal challenges, one filed by digital advocacy organization the Digital Freedom Project and the other by social news platform Reddit, represent a defining test of the sweeping online safety framework the Australian government enacted last December.
Led by New South Wales parliamentarian John Ruddick, the Digital Freedom Project submitted its constitutional challenge just weeks before the ban officially took effect on December 10, 2024. Though two teenage original lead plaintiffs, Noah Jones and Macy Neyland, have since stepped back from formal party status in the case, Jones is confirmed to attend the opening of proceedings this week. In prior comments to the BBC last November, Jones emphasized that while harmful content and predatory actors are undeniable risks on social platforms, a universal age-based ban is a poorly targeted, heavy-handed solution that misdirects resources. He argued that large social media firms should allocate their budgets to moderating harmful content and removing bad actors rather than diverting funds to avoid government penalties for non-compliance with the blanket age restriction.
Reddit’s parallel legal submission contends that the regulation poses profound, far-reaching risks to user privacy and fundamental political expression rights for young people, framing the mandate as a disproportionate overreach of state power. The policy, which is overseen and enforced by Australia’s dedicated eSafety Commissioner, imposes strict compliance obligations on 10 major platforms: Facebook, Instagram, TikTok, YouTube, Reddit, Snapchat, X, Kick, Threads, and Twitch. These services are required to implement “reasonable steps” to verify user ages and block access for anyone under 16, with penalties for serious or repeated violations reaching as high as A$99 million (approximately US$70 million). To date, no platform has been issued a fine, though the eSafety Commissioner has opened formal non-compliance investigations into Meta-owned platforms Facebook and Instagram, alongside Snapchat, TikTok, and YouTube. Messaging service WhatsApp, popular gaming platforms Roblox and Discord, and child-focused educational tools such as YouTube Kids and Google Classroom are explicitly exempted from the rules.
In the immediate aftermath of the ban’s implementation, Meta reported it had terminated roughly 500,000 underage user accounts across its platforms. However, widespread anecdotal accounts from young Australian users reveal that many have easily bypassed the mandated age verification checks, which range from requests for credit card information to government-issued photo ID and biometric selfies. The policy has sparked fierce national debate: supporters maintain the restriction is a critical safeguard to shield vulnerable children from cyberbullying, exploitative content, and online predators, while critics argue it is an overly blunt measure that undermines young people’s digital literacy and access to peer support, and that policy efforts should instead prioritize targeted improvements to content moderation and age-appropriate online safety infrastructure. Communications Minister Anika Wells has repeatedly reaffirmed the government’s unwavering commitment to the rule, stating last November that officials would not be “intimidated by big tech legal threats” and would stand firm in defending the policy on behalf of Australian families.
-
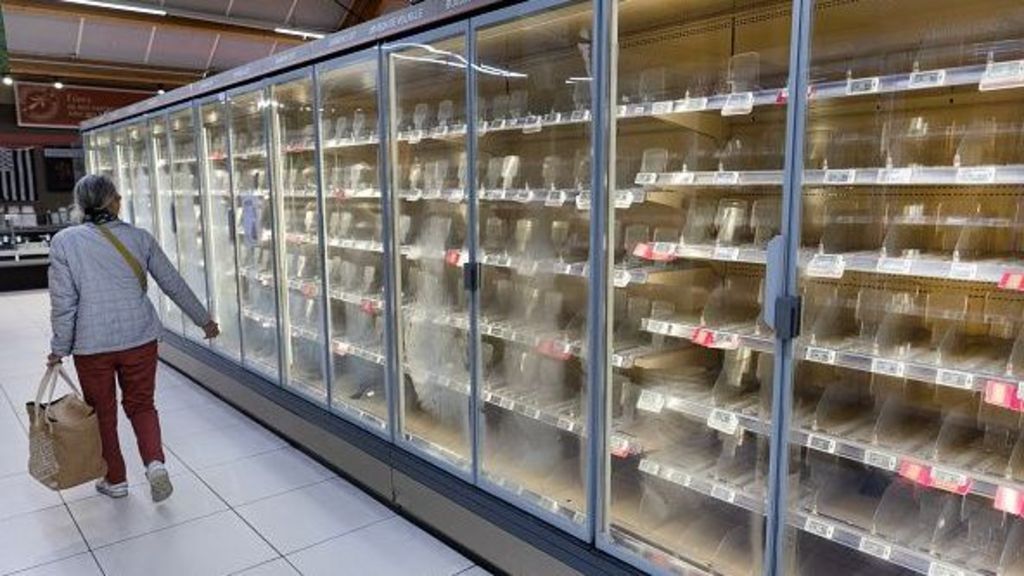
If hackers can take control of a supermarket freezer, how vulnerable is other tech?
A wave of suspected cyber-intrusions targeting supermarket chains across Europe has disrupted operations of commercial refrigeration and freezer systems, sparking widespread alarms over unaddressed security gaps in internet-connected hardware spanning industrial machinery to common household smart appliances. The expanding ecosystem of internet-linked devices, ranging from smart refrigerators, central heating systems, and washing machines to large-scale industrial control units, offers users the convenience of remote monitoring and adjustment, but every network-connected endpoint represents a potential entry point for malicious cyber actors. While major consumer technology brands typically invest substantial resources to fortify their products against unauthorized access, past documented vulnerabilities have underscored persistent risks: as far back as 2015, cybersecurity researchers proved they could intercept unencrypted internet traffic through a flaw in a Samsung smart fridge model. Crucially, investigators have confirmed no evidence links the recent November supermarket cyber-attacks to targeted exploitation of domestic consumer smart appliances. Ciaran Martin, former chief executive of the UK’s National Cyber Security Centre (NCSC), emphasized that device manufacturers bear greater responsibility for embedding robust security safeguards at the product design stage. “We need to demand far more accountability from large technology firms to deliver inherently secure devices and products from the outset,” Martin stated, while urging ordinary consumers to prioritize regular software updates and enable multi-factor authentication on all connected devices where available. “It may feel like a minor hassle, but these steps take only seconds to complete and drastically reduce exposure to risk.” Since April 2024, new UK regulatory mandates have legally required manufacturers of specified consumer smart devices to meet baseline cybersecurity standards, including enforceable rules for default password protections and long-term security update support. The NCSC confirmed it is collaborating with global allied agencies and private sector stakeholders to conduct full forensics on the recent European supermarket incidents, and has not detected any operational impact on retail infrastructure within the UK to date. However, analysis from UK Cyber Defence researchers has uncovered over 800 publicly accessible interfaces tied to refrigeration units and building management systems operated by British retail chains. While public accessibility does not automatically equate to exploitable vulnerabilities, these unsegmented connections create unnecessary exposure that bad actors could leverage via weak default passwords or unpatched software flaws. The UK government has already convened high-level discussions with leading food retail executives to bolster industry-wide cyber resilience, building on lessons learned from prior disruptive attacks. Helen Dickinson, chief executive of the British Retail Consortium, noted that cyber threats now rank among the top operational risks for the retail sector, with member businesses actively partnering with the NCSC to share real-time threat intelligence and reinforce defensive protocols. This is not the first time cyber intrusions have threatened national food supply chains: in May 2025, ransomware attacks targeting major UK retailers M&S and the Co-op severely disrupted fresh food delivery logistics, leaving large swathes of store shelves empty and prompting widespread customer complaints across the country. Tom Hegel, a senior researcher at cybersecurity firm SentinelOne, stressed that retail operators must clarify lines of accountability for connected on-site equipment. “Retailers cannot afford ambiguity over who holds ultimate responsibility for the cybersecurity of this hardware, rather than only clarifying who is tasked with physical repairs,” Hegel explained. He warned that the convenience of internet connectivity carries tangible, real-world risk when security frameworks lag behind functionality: “Once an attacker gains control of these operational systems, even standard, legitimate functions like automated defrost cycles can be weaponized to cause deliberate disruption. A single altered setting can destroy thousands of pounds worth of perishable physical stock, rather than merely disrupting a digital computer network.” The security risks extend far beyond retail and domestic consumer appliances, as networked connected technology now forms the backbone of remote management for industrial manufacturing equipment, commercial fleets, and critical public infrastructure. Renowned cybersecurity expert Ken Munro cited the landmark 2015 research demonstration where security teams remotely compromised a Jeep vehicle through its internet-connected infotainment system, a high-profile incident that spurred the entire global automotive industry to implement sweeping security overhauls for connected vehicle systems. “Thankfully, the automotive sector recognized the urgency of the risk and moved quickly to resolve these gaps,” Munro noted. Mobile internet connections are now also widely deployed to remotely monitor and adjust operations at power generation facilities and public water distribution networks, but Munro cautioned that security standards are uneven across different sectors and geographic regions. While large UK utility providers generally maintain robust protections for these critical connected systems, his greatest concern centers on smaller, underfunded utility operators that continue to rely on outdated, unpatched legacy equipment with well-documented vulnerabilities. Olivier Daloy, a cybersecurity expert at global firm Zscaler, echoed these warnings, noting that without standardized, mandatory security safeguards, every internet-linked facility and piece of equipment – from automotive manufacturing plants to electricity grids and public transport networks – faces comparable risks of disruptive, financially damaging cyber intrusions.
-
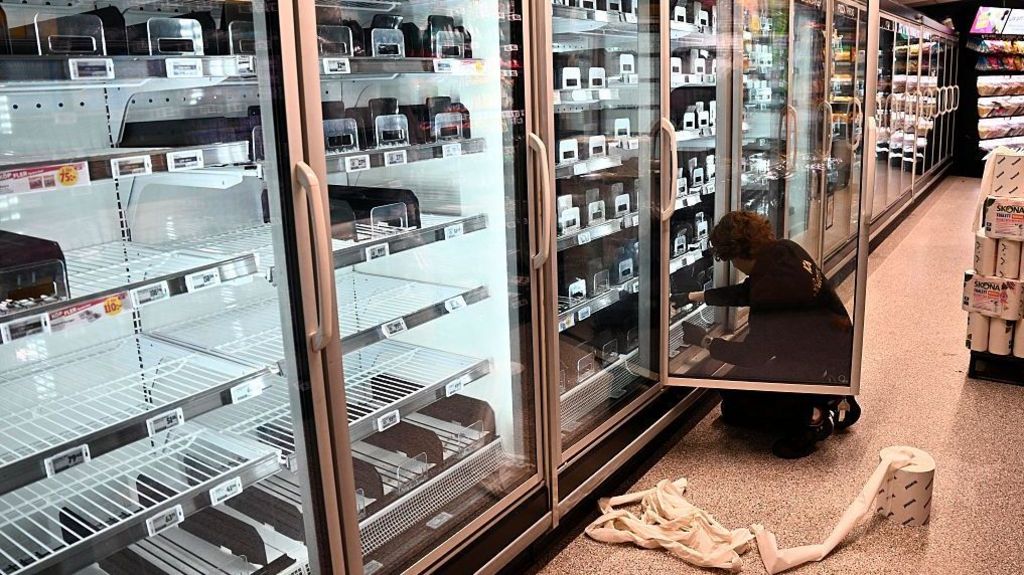
Supermarket freezers in Belgium and Sweden hit by cyber-attack
A coordinated cyber incursion targeting connected commercial refrigeration infrastructure has crippled operations at dozens of grocery outlets spanning Belgium, Sweden, and Ireland, forcing retailers to discard massive volumes of frozen and chilled perishables after threat actors maliciously adjusted temperature controls to dangerously high levels. The widespread digital breach follows a nearly identical incident that compromised hundreds of French supermarket locations just one month prior, though law enforcement and cybersecurity teams have not yet publicly identified the perpetrators behind this latest cross-national campaign. In Belgium, two of the country’s largest grocery chains reported widespread disruption: 40 locations under leading domestic retailer Delhaize suffered overnight system failures that rendered their cooling units unresponsive, while 15 Belgian outlets of multinational giant Carrefour confirmed their technical teams are conducting full forensic analysis of the breach to trace the attack vector. Across the North Sea in Sweden, multiple independent ICA grocery stores operating outside the brand’s centralized corporate network fell victim to the hack, with one ICA location in the southern town of Sjöbo posting a public warning on social media that hackers had cranked freezer temperatures all the way to 50°C (122°F) in the middle of the night. The Sjöbo outlet temporarily shuttered to dispose of spoiled stock before resuming normal customer operations, while ICA’s corporate headquarters stated it is deploying dedicated support teams to assist all impacted franchise locations. Separately, 7 of Sweden’s 800 Coop supermarket locations were hit, with brand representatives confirming to the BBC that the incident has been fully contained and no further outlets are at immediate risk. In Ireland, 13 SuperValu stores also reported disruptions to their refrigeration systems linked to the same attack pattern. Local media estimates indicate thousands of euros worth of frozen and chilled food, ranging from frozen meat and dairy to pre-prepared meals, had to be completely discarded to avoid public health risks, as the extreme elevated temperatures rendered all perishable inventory unsafe for human consumption. Industry cybersecurity analysts note that the attack exploits the relatively weak security protections often deployed on internet-connected building management systems in retail settings, which are frequently not segmented from broader store networks or protected with the same rigorous safeguards used for point-of-sale and payment processing infrastructure.
-
Crypto worth billions frozen after suspected Binance hack
On Thursday, global cryptocurrency industry leader Binance announced it has locked down approximately $3 billion in digital assets to block unauthorized access and potential theft, as the platform launches a full-scale probe into an emerging critical security vulnerability. The exchange, which ranks first globally by daily trading volume, simultaneously paused all user deposit and withdrawal operations across its system while internal cybersecurity teams run comprehensive safety audits, and publicly committed that it will absorb 100% of any financial losses stemming from the incident, with no user funds at risk. Changpeng Zhao, the exchange’s founding former CEO who retains majority ownership of Binance, confirmed via public statements that the unfolding situation strongly indicates a targeted hack against the platform. In a coordinated cross-industry response, two of the world’s largest stablecoin issuers have also taken urgent action: Tether, the operator of top-pegged crypto USDT, has frozen roughly $1.6 billion in assets tied to the suspected breach, while Circle, co-creator of the widely used USDC stablecoin, has locked down over $800 million in related funds, bringing the total cross-platform frozen asset value to nearly $5.4 billion. Circle CEO Jeremy Allaire noted that his team is conducting real-time monitoring of all developments linked to the Binance exploit to mitigate broader industry risk, while Tether CEO Paolo Ardoino emphasized that safeguarding the broader crypto ecosystem and its partner platforms is his firm’s top operational priority during the crisis. Binance leadership stated that the total value of seized assets is likely to rise as its cybersecurity teams collaborate 24/7 with global law enforcement agencies and industry partners to trace, identify, and secure additional funds connected to the suspected malicious activity. The exchange has urged all users to rely exclusively on verified official Binance communication channels for real-time updates, and promised to release a full public post-mortem report detailing the root cause of the incident once the investigation concludes. News of the suspected breach sent immediate shockwaves through the broader cryptocurrency market: Bitcoin’s spot price dropped roughly 5% in hours following the first public alerts, while leading altcoins including Ethereum and Solana recorded even steeper double-digit percentage dips in early trading. Multiple independent crypto security researchers and industry analysts had flagged unusual on-chain activity and warned of a potential large-scale breach targeting Binance several hours before the exchange issued its formal public confirmation. The full scope and total unauthorized fund exposure of the attack remain unconfirmed at this stage. The incident draws parallels to the 2025 high-profile breach of Dubai-based crypto exchange Bybit, in which North Korea-linked hacking groups stole a record $1.5 billion in digital assets, prompting renewed industry-wide scrutiny of cross-platform security protocols and coordinated threat response frameworks.
-
Microsoft profits soar days after announcing thousands of layoffs
Global technology behemoth Microsoft has unveiled blowout quarterly financial results for the fiscal period ending September 30, posting a net profit exceeding $36.6 billion, a milestone that comes just days after the firm announced a targeted voluntary separation program for roughly 60,000 employees as part of a broader cost realignment strategy to free up capital for its aggressive artificial intelligence expansion. Announced earlier this week, the voluntary buyout scheme is extended to eligible staff across core markets including the U.S., UK, Canada, and India, designed to right-size the 220,000-person global workforce to align with evolving operational priorities, while departing employees will receive severance packages and dedicated career transition support. Driven by explosive 30% year-over-year growth in its Microsoft Cloud enterprise services portfolio, the company’s total quarterly revenue hit $92.3 billion, marking a 19% uplift from the same 12-month period prior. Following the earnings announcement, Microsoft’s stock climbed nearly 2.9% in New York after-hours trading, a sharp contrast to peer Alphabet, which saw its share price plummet 9.75% the same day after reporting a 25% year-over-year drop in quarterly net profit that left investors underwhelmed despite its own ongoing heavy AI spending commitments. Chief Executive Officer Satya Nadella emphasized that the company’s ongoing AI development roadmap has driven widespread cross-industry adoption of the technology, delivering tangible, real-world value for enterprise and consumer users alike. While the strong results beat market analyst expectations, Microsoft openly acknowledged lingering financial risks tied to the massive, multi-billion-dollar ongoing investments in AI infrastructure, including specialized semiconductors and new data center capacity. The earnings update arrives amid a broader industry trend where top-tier tech giants including Amazon, Meta, and Alphabet are on track to collectively pour more than $700 billion this year into AI-related hardware and infrastructure, a spending spree that has left investors closely scrutinizing long-term return on investment prospects to assess whether the unprecedented capital outlay is sustainable over coming quarters.
-
Apple to replace iPhone Duos affected by screen problem
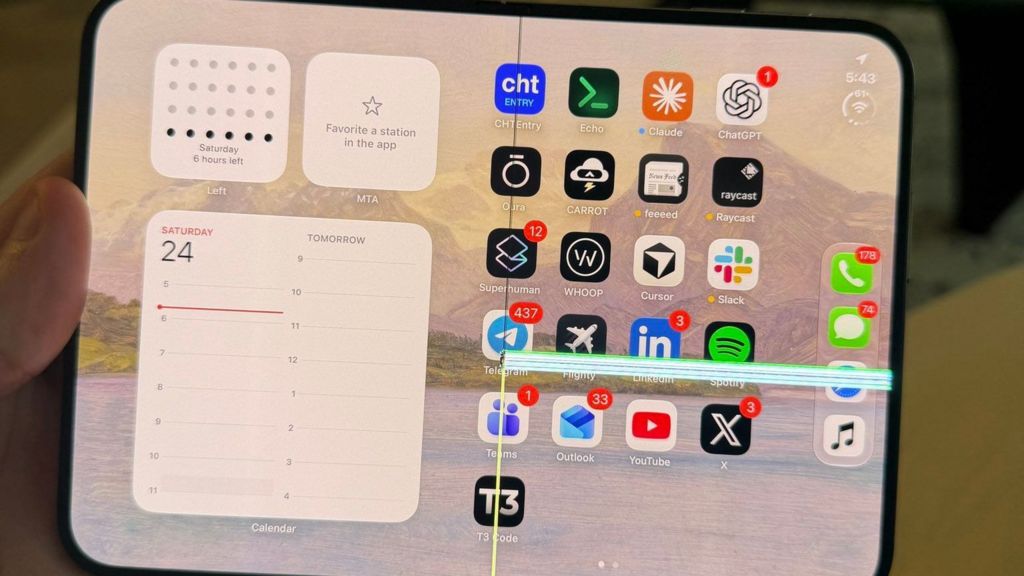
Just days after Apple’s highly hyped first-ever foldable smartphone, the iPhone Duo, hit global retail shelves, the tech giant has publicly confirmed that a small subset of the premium devices are experiencing critical inner display malfunctions. Priced starting at £1,999 ($2,668) in the UK and topping out at £3,199 for highest-spec configurations, the landmark product represented Apple’s most ambitious iPhone redesign in nearly 20 years, unveiled by newly appointed CEO John Ternus shortly after he succeeded Tim Cook in September.
Social media posts from early adopters have circulated widely in recent days, showing visible vertical line artifacts across the Duo’s 7.6-inch inner foldable display, alongside user reports of unexpected crunching sounds when unfolding the device and structural cracks forming along the central hinge crease. One New York-based user, Justin Lokos, shared photos of his flawed unit alongside a full replacement provided on-site by local Apple store staff, thanking the team for their fast support. Apple’s official statement advised all affected customers to reach out directly to the company to arrange free replacement services, but declined to disclose exact figures for the number of impacted units.
Notably, some of the circulating imagery of damaged Duo devices has been flagged as AI-generated, clouding efforts to quantify the scale of the manufacturing defect. Francisco Jeronimo, leading technology analyst at global market research firm IDC, emphasized that stakeholders should exercise caution before drawing sweeping conclusions about the entire production run, but noted that the early fault reports underscore that even a company with Apple’s unmatched engineering resources and rigorously managed global supply chain faces a steep learning curve when breaking into the foldable device segment.
The complex central hinge mechanism that enables the Duo to flip open like a small tablet is a well-documented pain point for the entire foldable industry: Samsung, Apple’s top rival in the space, faced a major public setback with its original Galaxy Fold back in 2019, when pre-launch reviewers reported widespread screen failures on early test units. Jeronimo added that as Apple has positioned the iPhone Duo as a far more polished, premium alternative to the years-old lineup of Android-powered foldables already on the market, the company’s response to these first-generation teething issues will not only shape its own sales performance, but also long-term consumer trust in the entire foldable smartphone category. With the iPhone Duo set to launch in 28 additional global markets on October 30, the analyst urged Apple to formalize and communicate its explicit warranty coverage for hinge and screen defects quickly to avoid eroding confidence among its large, loyal customer base.