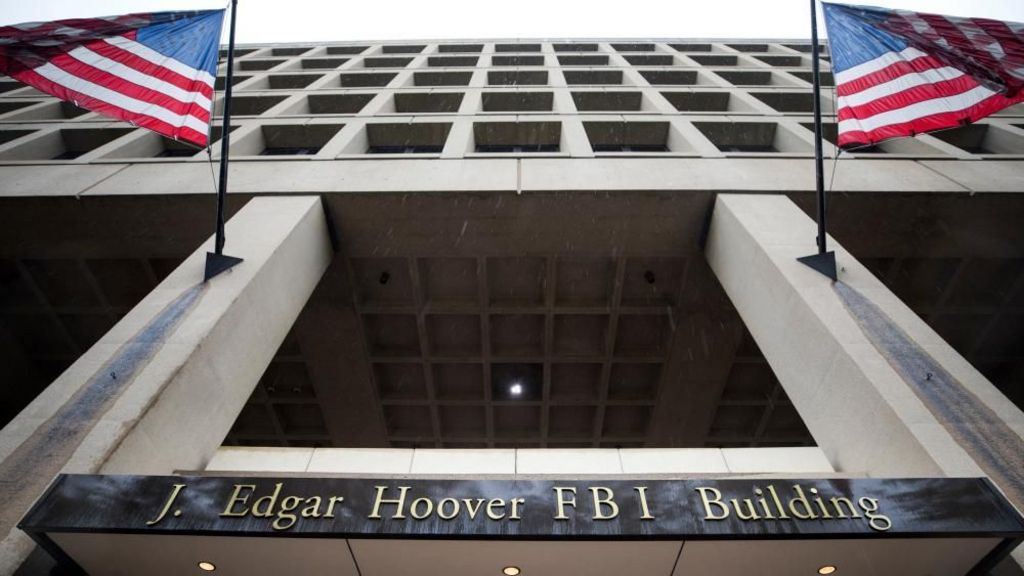
U.S. federal law enforcement authorities are conducting an active investigation into a suspected unauthorized intrusion that targeted the FBI’s core criminal information repository, multiple U.S. mainstream media outlets have confirmed via anonymous sources with direct knowledge of the ongoing review. The compromised system, formally known as the National Crime Information Center (NCIC), serves as a critical shared platform utilized by every tier of U.S. law enforcement, from small local police departments to federal agencies, to circulate real-time data on active arrest warrants, firearm background check records, missing person files, and other sensitive public safety records. As of press time, the British Broadcasting Corporation has reached out to the FBI’s public affairs office to request official clarification and comment on the reported breach, but no formal statement has been released to the public.
The emerging potential security incident unfolds in the immediate aftermath of a cascading series of widespread technical disruptions that crippled operations across multiple high-stakes U.S. critical infrastructure sectors last week, including major banking networks, national air traffic control systems, and key utility and public service platforms. Federal regulatory and homeland security officials have previously concluded that those widespread service outages were not triggered by malicious cyberattacks, but the cascading disruptions have already drawn intense bipartisan scrutiny from U.S. congressional lawmakers, who have launched oversight inquiries into gaps in national critical system cybersecurity.
The cybersecurity leadership shakeup at the highest levels of the U.S. government also unfolded this week, when White House National Cyber Director Sean Cairncross was removed from his post. U.S. President Donald Trump publicly stated that the dismissal was tied to Cairncross’s underperformance in his role overseeing national cyber defense strategy.
This is far from the first time the FBI itself has been targeted by malicious cyber actors. Back in September of this year, the bureau publicly confirmed it was probing a high-profile intrusion carried out by the notorious cybercriminal collective ShinyHunters, which publicly claimed to have exfiltrated full sensitive personal data for all roughly 38,000 active FBI personnel. In the wake of that September breach, a retired senior FBI agent told the BBC that the exposed personal identifying information of current field agents and analysts posed a severe, tangible safety risk, as the data could easily be exploited by organized criminal networks or hostile foreign state-sponsored hacking groups to target, track, or coerce active law enforcement personnel.
In a parallel separate cybersecurity development, NBC News has reported that the U.S. Department of Agriculture (USDA) also faced an apparent targeted cyberattack, with internal agency notifications sent to staff on Thursday confirming that the agency’s core farm payment processing system had been accessed by unauthorized parties. At time of publication, the USDA has not issued any public statement to confirm or deny the reported intrusion, nor has it shared details on potential disruption to agricultural subsidy disbursements to U.S. farm operators.